
Security & Compliance
Secure By Design, From the Front Door to the Data.
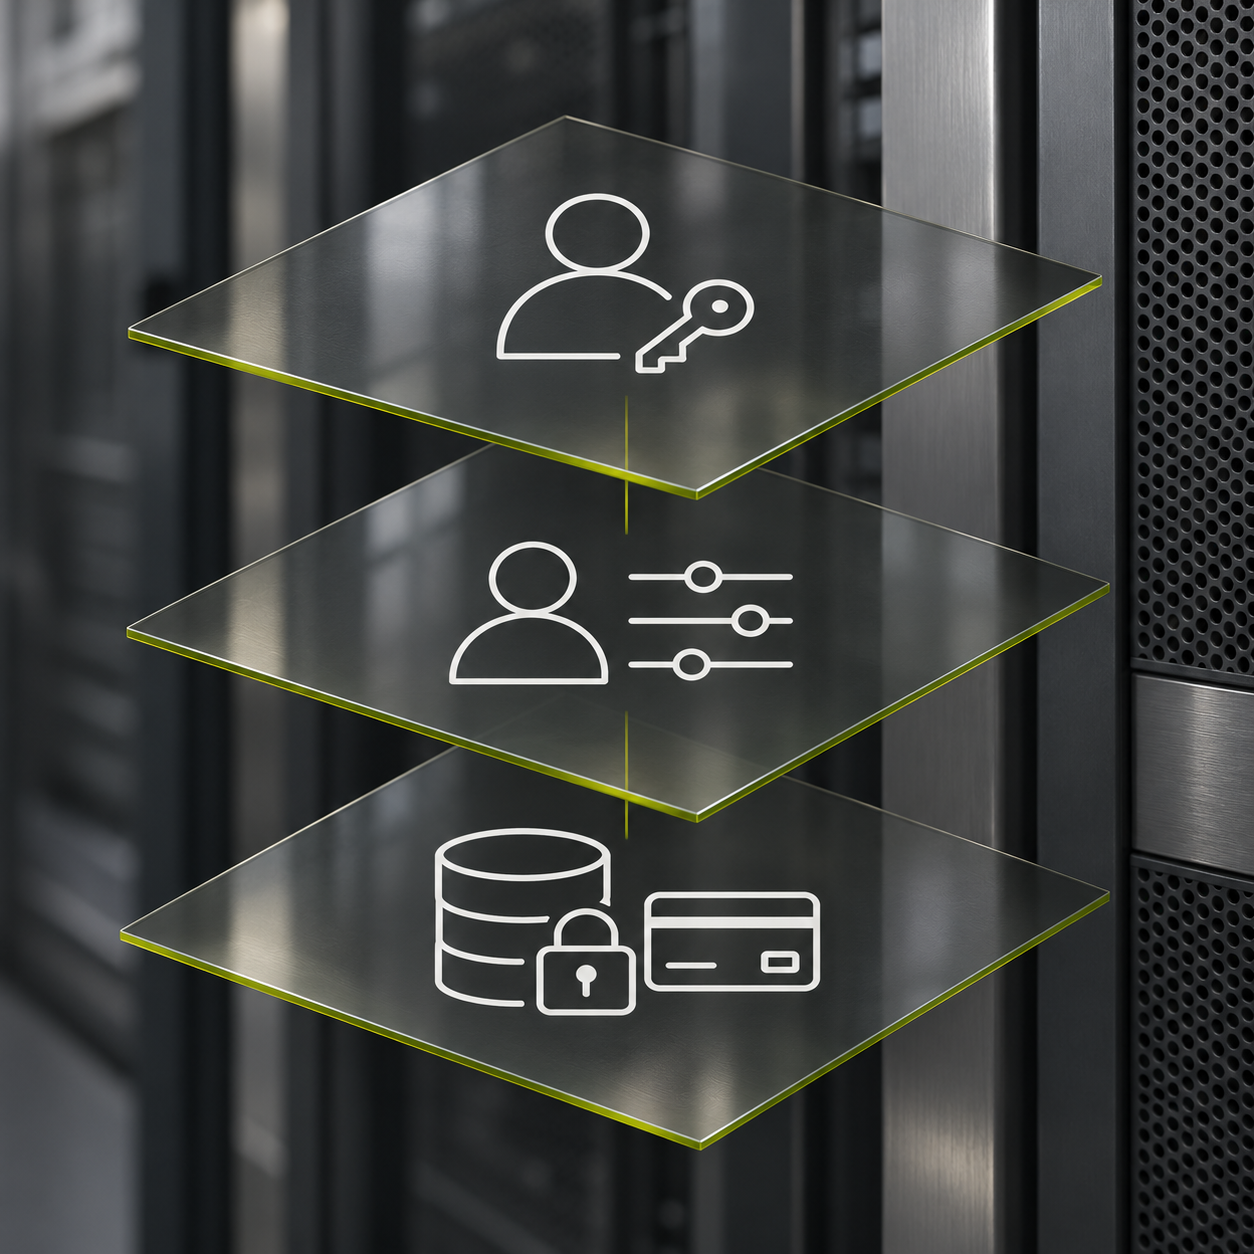
QuickBrand protects your store at three layers: who can get in, what each person can see, and how every payment and personal record is handled.
We take the trust brands place in us seriously. When you put your logo and your people on our platform, protecting both is our job — not a box we check for the IT review.
SOC 2 Type I & II
Independently audited and compliant
PCI-DSS via Stripe
SSO · Purchasing · Permissions
GDPR
Privacy and data retention, no remarketing
Single sign-on
Okta, Microsoft Entra ID, OAuth
100% SSL
Every page, every session, encrypted
Control Who Gets in, And What They See.
A company store is only as safe as its front door. QuickBrand gives you three sets of tools to decide who can enter, what each person sees once they're inside, and how fast you can change your mind.
Access controls
Who can get in
Security groups
What each person can see
Security groups
What each person can see
Keep Unauthorized Users Out — From Day One.
Restrict by email domain or site password
Only people with your company email domain — or the password you set — can view the store. We help you set it up so the wrong people never see your catalog, your pricing or your logo.
Single sign-on or a passwordless Magic link
Your people sign in with the company credentials they already use through single sign-on, or with a one-time Magic Link sent to their email. No new password to remember, reuse or leak.
Registration alerts and approvals
Turn on alerts to hear the moment someone creates an account, and approvals to decide who gets in. Real-time control over who joins your program — optional, and yours to switch on.
Everyone Sees Exactly What They Should. Nothing more.
Role-based permissions control the products, categories, payment methods, shipping methods and logos each person can see. Your field team sees their uniform catalog. Your marketing team sees event gear. Your approvers see the bill-to option nobody else should.
It's one store with as many views as your organization needs — and a lot fewer "why can I order this?" emails.
One store, two groups
Illustrative example
| Corporate buyers | Field staff | |
|---|---|---|
| Products | Full catalog | Uniforms & PPE |
| Categories | All | Workwear, Safety |
| Payment methods | Bill my department, card | Uniform allowance credit |
| Shipping methods | Ground, expedited | Ground to branch |
| Logos | Corporate + sub-brands | Field logo only |
Same store, same URL. Each person sees only what their group allows.
Your Store, Your Call — in Real Time.
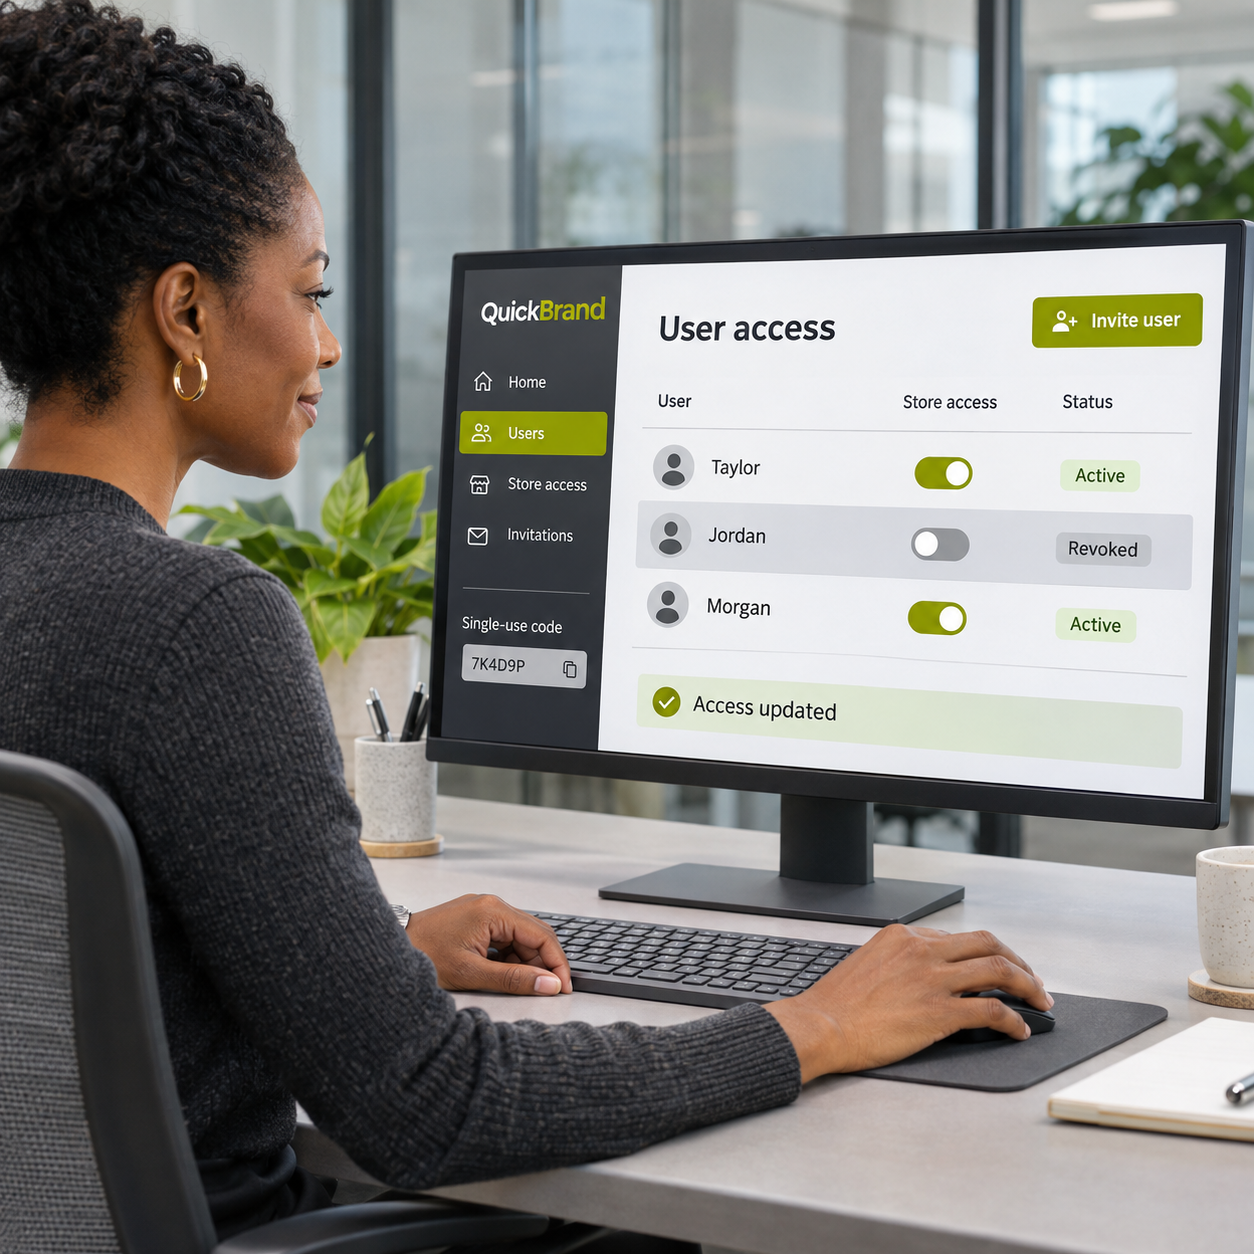
When someone leaves your team, their store access shouldn't wait on a support ticket. Your own customer admins hold the keys.
See users in real time, revoke in one click
Customer admins see live customer data for their store and can remove any user's access with a single click.
User Invites with one-time codes
Send a unique, single-use code to each person you want on the store. Once it's used to create an account, it can't be used again.
How QuickBrand Secures Your Data.
Behind every storefront is the part nobody sees: how payments are processed, how personal information is handled, and how the platform itself is protected and audited.
Financial data
Card payments processed by Stripe
Credit card payments on QuickBrand run through Stripe, a PCI-DSS Level 1 certified payment processor.
GDPR compliance
QuickBrand follows GDPR requirements for user data privacy and data retention — collected for a reason, kept only as long as it's needed.
User data
PCI-DSS compliant and token-based
Card details are replaced with secure tokens, so card numbers are never stored on QuickBrand. Our Attestation of Compliance (AOC) is available on request.
No sharing, no remarketing, no off-site tracking
We never share or remarket your users' data to third parties, and we don't follow them around the web. Their information is used to run your store and deliver their orders. Your people are your people — not our audience.
Platform security
100% SSL-secured traffic
Every page and every session on QuickBrand is encrypted in transit with SSL/TLS. No exceptions.
SOC 2 Type I and Type II audited
Independent auditors have confirmed both that our controls are designed correctly (Type I) and that they work as designed over time (Type II).
Identity verification through single sign-on
Verify every user against your own identity provider: Okta, Microsoft Entra ID, or OAuth-based providers.
Running a vendor security review?
We've been through plenty of them, and we'd rather make yours easy than make you chase us. Tell us what your IT or procurement team needs and we'll get it to you.
Security Questions, Answered.
-
Yes. Restrict access by email domain or a site password, require single sign-on, or invite people individually with one-time codes. Registration approvals let your admins approve every new account before it's active.
-
No. Card payments are processed by Stripe and handled as secure tokens, so card numbers are not stored on QuickBrand. Our PCI-DSS Attestation of Compliance is available on request.
-
QuickBrand supports single sign-on through Okta, Microsoft Entra ID and OAuth-based identity providers. Tell us what your organization uses and we'll confirm the setup.
-
Immediately. Customer admins can revoke any user's access with a single click — no ticket and no waiting on us.
-
Yes. Security groups control which products, categories, payment methods, shipping methods and logos each user sees. Users can be placed into groups automatically by email domain or by entering a security code.
-
No. We don't share or remarket user data to third parties, and we don't track users off-site. User data is handled in line with GDPR requirements for privacy and retention.
-
Yes. QuickBrand is audited and compliant for both SOC 2 Type I and SOC 2 Type II.
Have A Security Review on Your Desk?
Send us what your IT team is asking for. Your Account Manager will come back with documentation and straight answers — and if we don't do something, we'll tell you.